Burner notes: encrypted links with view limits
Share a separate encrypted copy of a note body through a link. Choose an access allowance and expiry, or revoke it when it should no longer be available. These controls block future retrievals; they cannot erase content a recipient has already opened or copied.
Reviewed 12 November 2026
The short answer
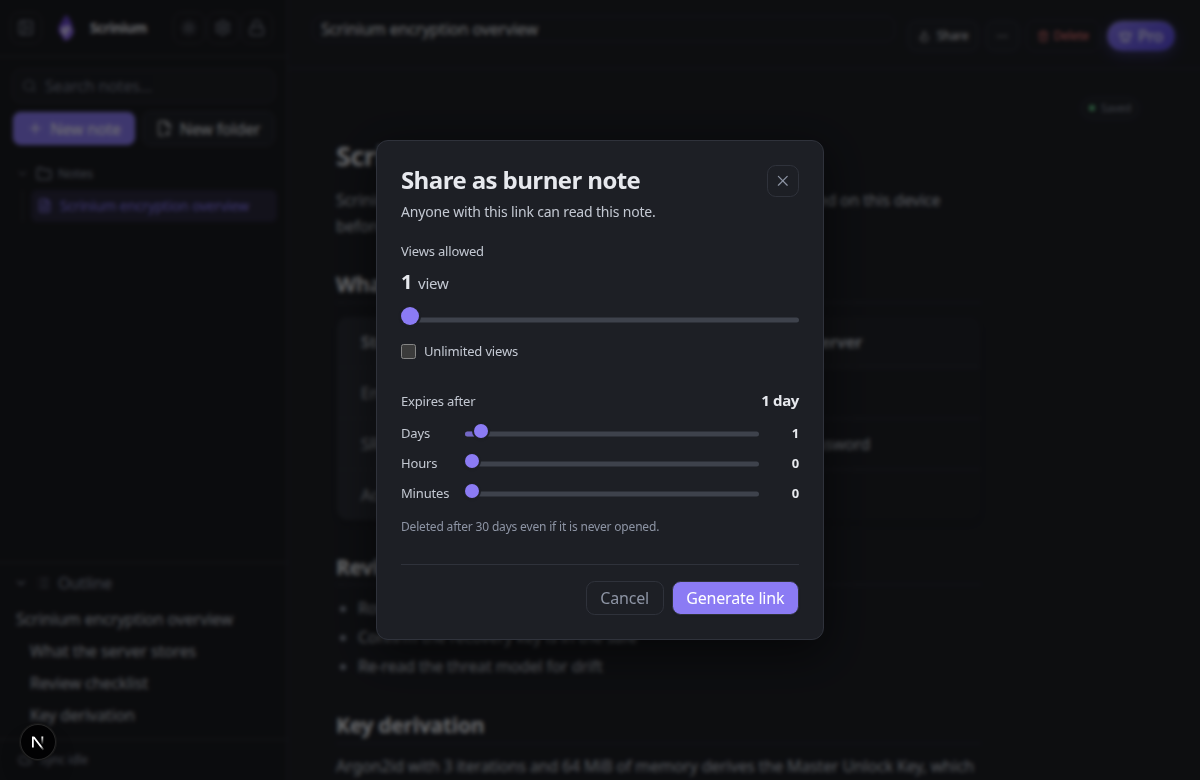
Burner notes are a Pro and Supporter feature. Open a note and choose Share, set Views allowed and Expires after, then generate and copy the link. The browser encrypts a separate text copy with a fresh key. The recipient uses the complete link without an account. Expiry, used views and revocation block later retrievals; cleanup of stored records is separate. An already loaded page, screenshot or copied text can remain.
When an expiring link is useful
A handoff note may only need to be available briefly. A link can keep its full text out of the conversation and provide a way to stop future access. It still needs a private channel: the complete address carries the decryption key.
Check the recipient and the scope of the content before sharing. This is a text-sharing workflow, not a claim that email or chat are always unencrypted, nor a guarantee that the reader cannot keep a copy.
How does a burner note work?
- 1. Choose Share. This creates an encrypted snapshot of the current note body. The original remains separate; its later edits do not change the shared text.
- 2. Set the access allowance and expiry. The dialog defaults to one view and one day. Leave Unlimited views unchecked for a one-view link.
- 3. Generate and copy the complete link. The secret key is in the fragment. The management list cannot show the full link again, so copy it before closing the dialog.
- 4. The recipient opens it in a browser. A successful ciphertext retrieval consumes an allowance before decryption. It is not a verified reader count; do not open your own one-view link to test it.
- 5. Later retrievals are blocked. Expiry, an exhausted allowance or revocation makes a later fetch fail. Already loaded content can remain readable, and maintenance cleanup is separate.
Why is the key in the link fragment?
The link has the shape /burn/#id.key. The fragment is omitted from the initial page request. The page then uses the id to request the encrypted note from the API and uses the key locally to decrypt it.
The full link can still be read by the recipient’s browser, page scripts and services it is pasted into. Do not publish it or assume that putting a key after # protects it from every tool. The threat model explains the limits of browser-based encryption.
What are burner notes used for?
Send the text intended for one recipient without putting the full note body into a conversation.
Limit future retrievals by time or access count. Share the complete link only with someone you trust.
Create an encrypted snapshot of the current note body. Edits to the original do not update that shared copy.
Keep the original in your vault while managing the shared copy separately. Burner links are not a file-sharing or collaboration feature.
What do burner notes not protect against?
Screenshots, photographs and copied text remain possible. Expiry and revocation do not remotely erase an already loaded page.
One view means a successful retrieval, not one verified person. A preview or scanner that opens the complete link and runs the page may consume the allowance.
Expired and exhausted links reject later retrievals. Stored records are removed separately by maintenance cleanup; do not treat a failed fetch as proof that every copy disappeared.
Creating burner notes requires Pro or Supporter and connected sync. Basic notes, encrypted sync and local search remain free.
Questions people ask
What is a burner note?
An encrypted text copy shared through a link with a view allowance and expiry. In Scrinium, later retrievals fail after the allowance or time runs out. The original note and any reader copies are separate.
Why is the key in the link fragment?
The fragment after # is omitted from the initial page request. Scrinium reads it in the browser, sends the note id to fetch ciphertext and decrypts locally with the key. Anyone with the complete link can attempt to read the note while access remains.
Can I revoke a burner note?
Yes. Open More Pro features, choose Manage burner notes and use Revoke. This blocks future retrievals, but does not erase text already loaded or copied by a recipient.
Is an expiring link the same as deleting every copy?
No. Expiry and used-up views block later retrievals. Physical cleanup of stored records happens separately, and neither expiry nor revocation can remove screenshots or copied text.
Can someone read it without a Scrinium account?
Yes. Recipients open the complete link in a browser. Creating the link requires Pro or Supporter and a connected sync account; receiving it does not require a recipient account.
Creating burner notes requires Pro or Supporter. Basic notes and encrypted sync are free.